Is your email, username, phone or password already leaked?
A self-hosted exposure checker that answers with evidence from 18 keyless sources โ
no API keys, no AI, no data leaving your machine.
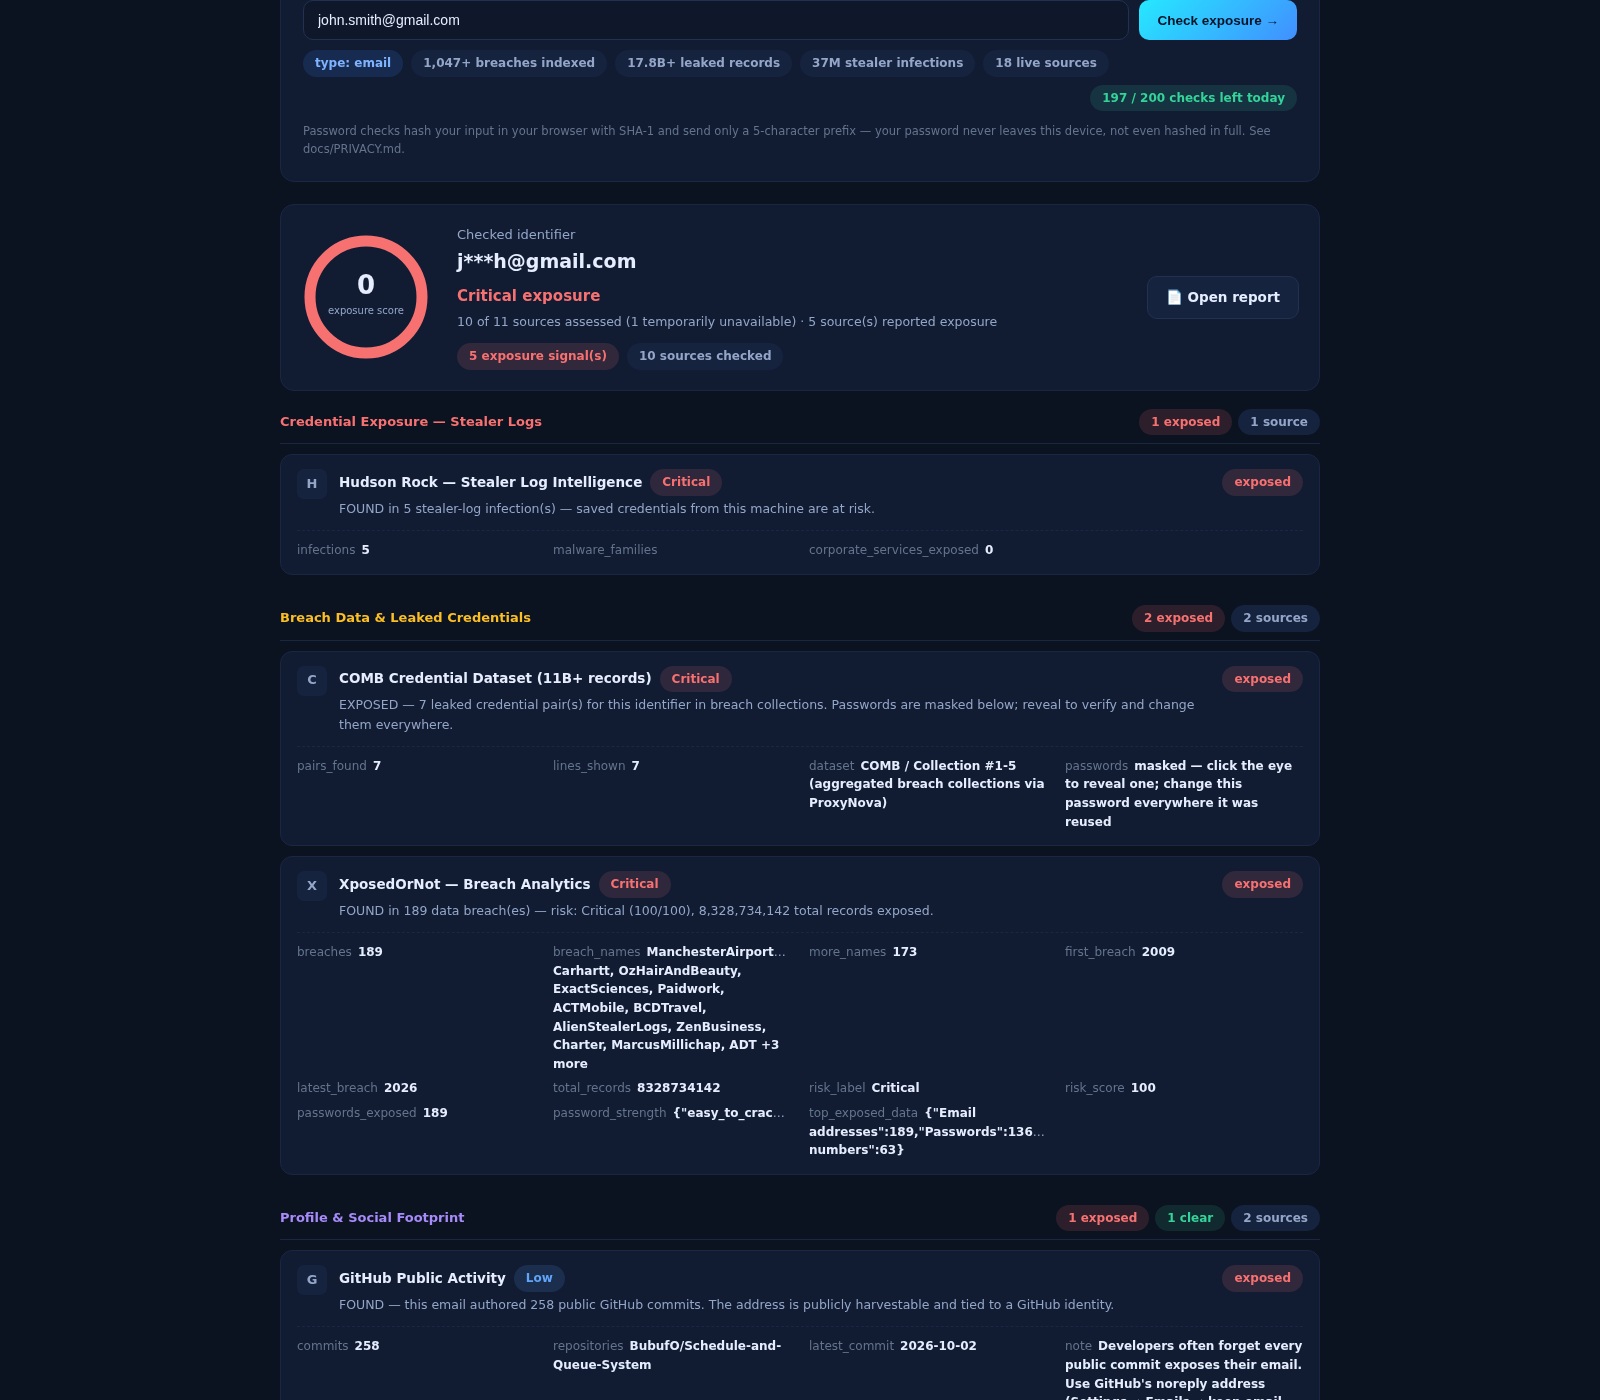
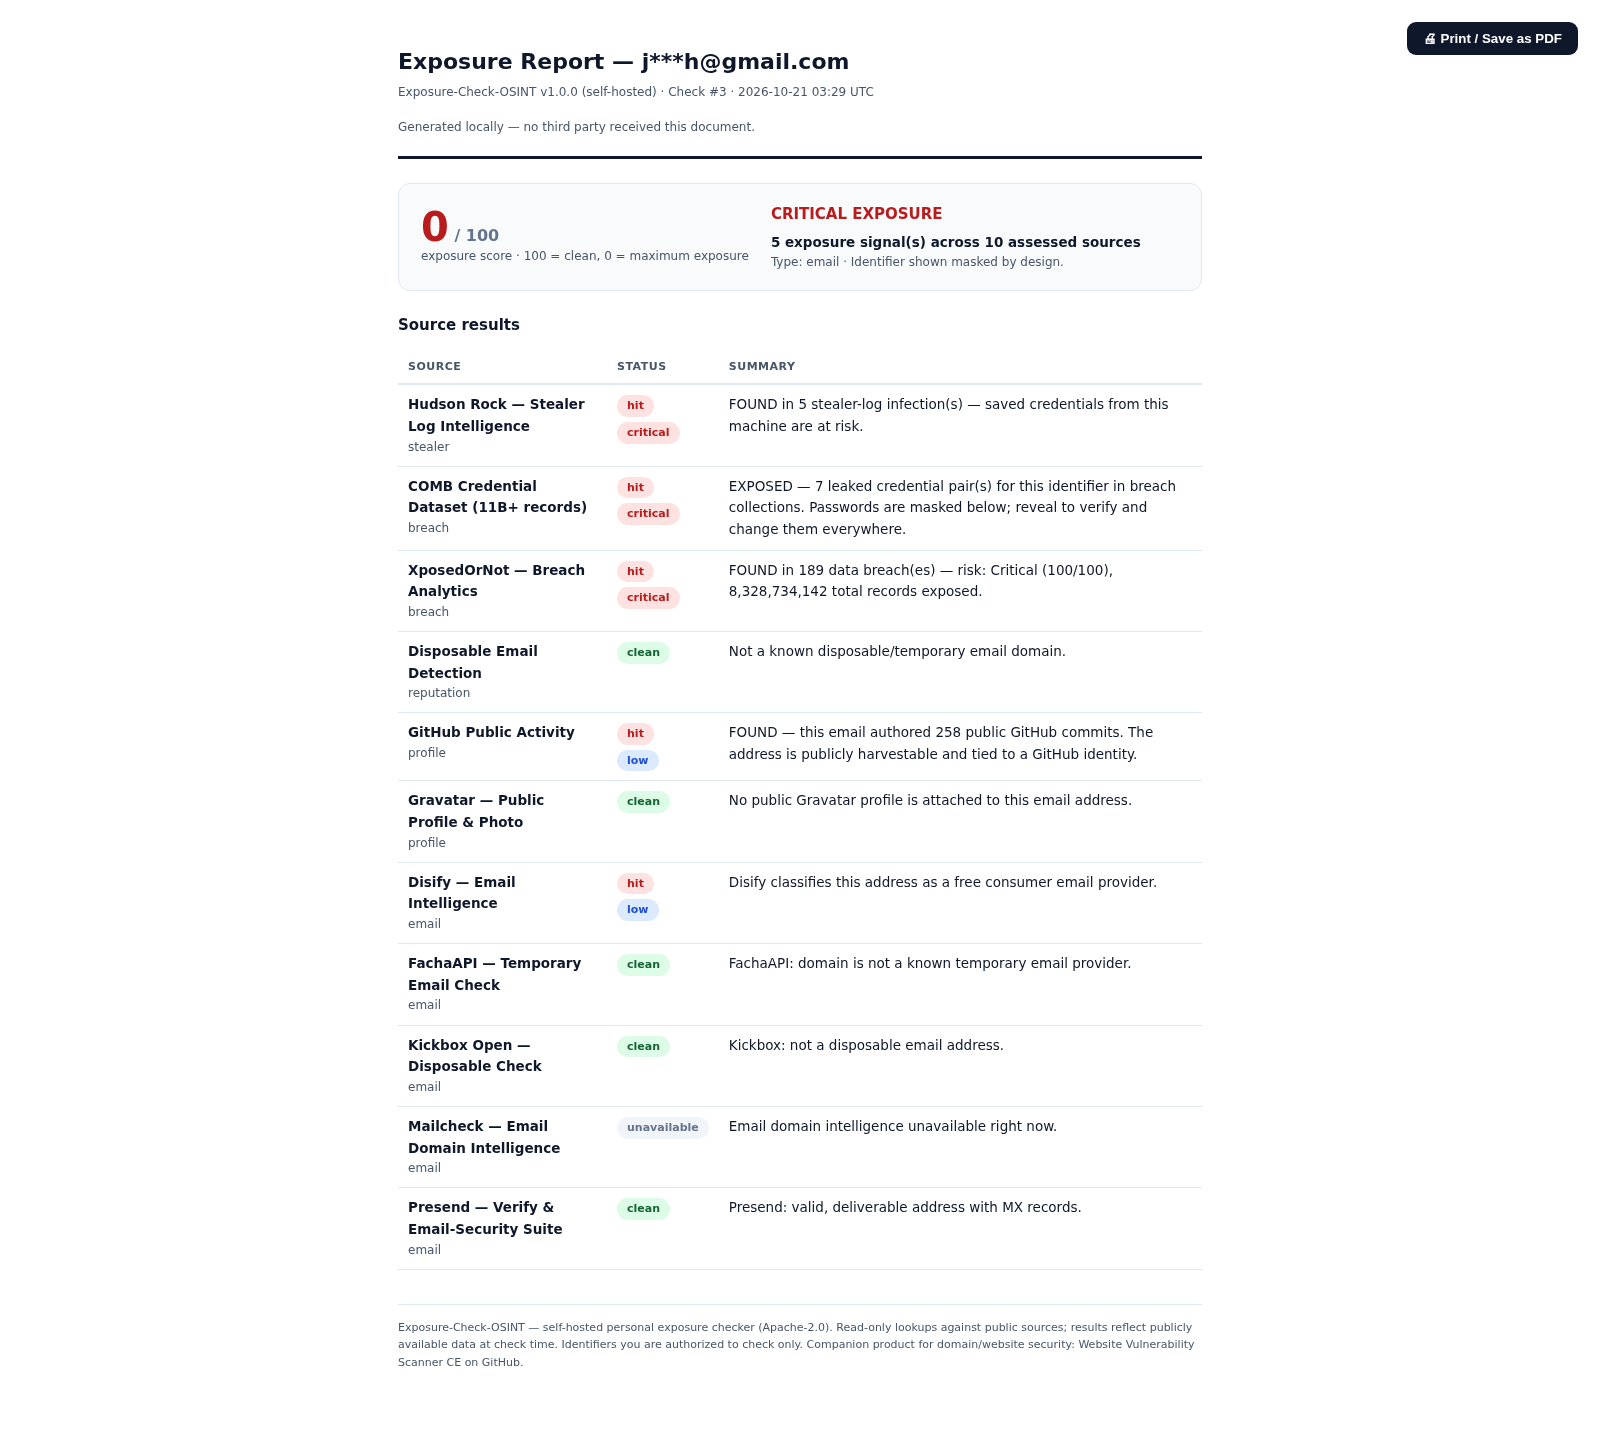
Every screenshot below is captured from a real running install โ live sources, live verdicts, real exposure.
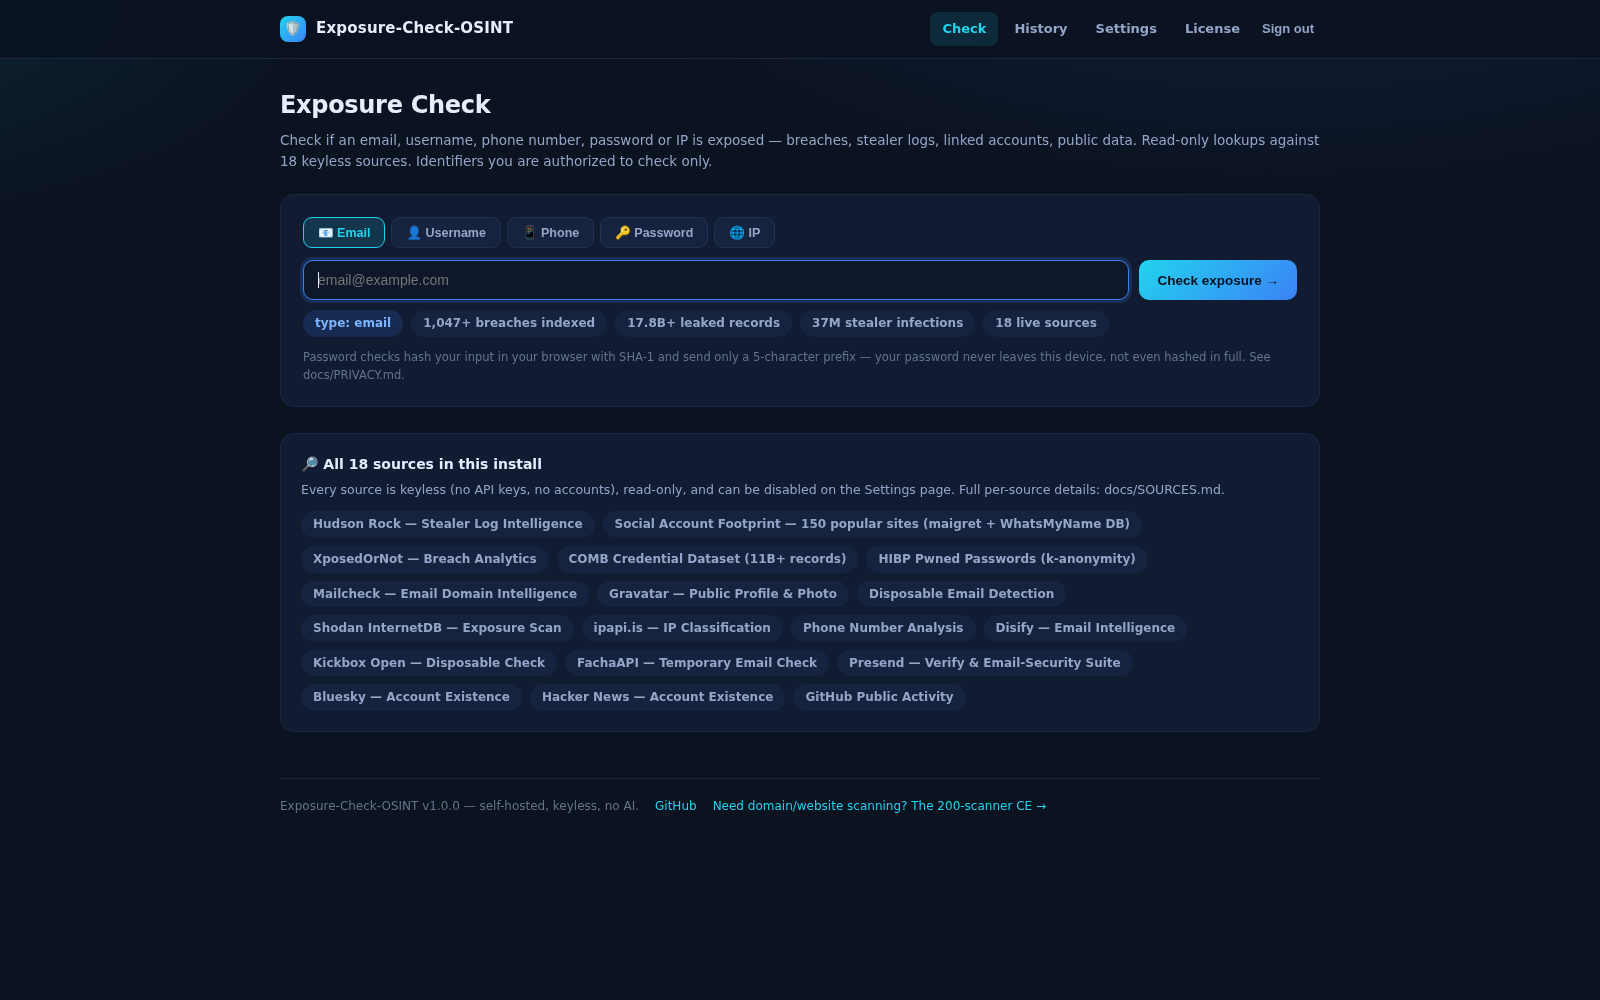
Personal identifiers, not domain scanning โ that's the scanner CE's job. This tool answers one question: what do attackers already know about you?
Breach collections, stealer-log infections, disposable flags, public-code associations
Which of 150 platforms carry this name โ logo grid, Bluesky, Hacker News, GitHub
Validity, country, line type, COMB leak association
HIBP Pwned Passwords with k-anonymity โ only a 5-char hash prefix ever leaves your browser
Open ports (Shodan InternetDB), VPN / proxy / hosting classification
No API keys to buy, no accounts to create, no rate-limit roulette. If a source is down it says so โ it never fakes a "clear".
Evidence found โ the source returns real matches, masked in the UI and stripped of credential material before storage.
The source answered and found nothing. A real answer, not a guess.
The source is down or blocked. It never counts as "clear" โ honesty over cosmetics.
Docker pulls a single container (Apache + PHP 8.3 + SQLite). Nothing else. Your data stays on your disk.
# 1. clone & launch โ http://localhost:8090 git clone https://github.com/RanaKhan77/Exposure-Check-OSINT.git cd Exposure-Check-OSINT && docker compose -f docker/docker-compose.yml up -d # 2. sign in (password set on first boot) and check yourself # 3. that's it โ no keys, no accounts, no telemetry
Identifiers stored as salted hashes + masked forms only. Password checks store nothing โ matching happens in your browser.
Every verdict is a deterministic, reproducible HTTP lookup. No model, no bill, no hallucinated findings.
Exposure score 0โ100 (100 = clean). Dead sources degrade honestly and never fake a pass.
Overview, install, privacy design, source attribution and FAQ โ as PDFs on the releases page.